

Breaching a Water Treatment Facility: A Physical Security Test
by Patrick Laverty on August 12, 2026 at 9:56 AM
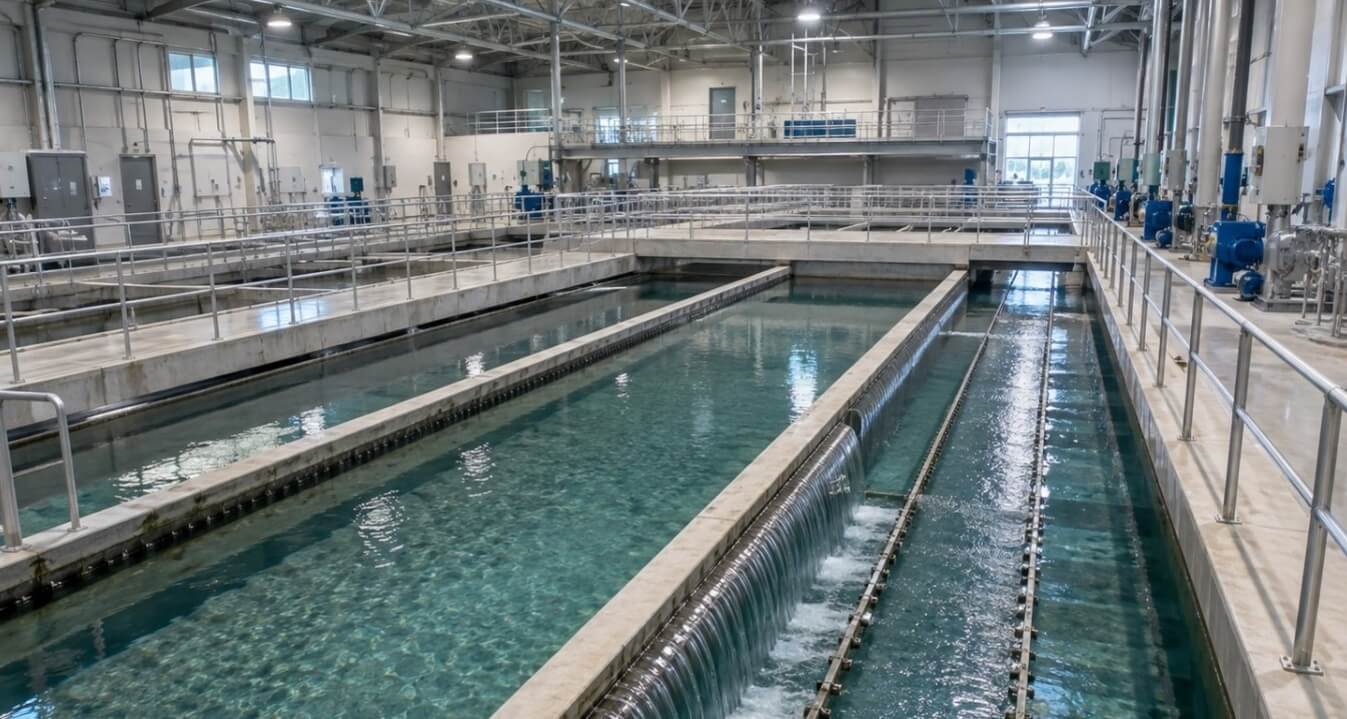
Most water utilities invest heavily in network penetration testing and web application security, and rightly so. Far fewer test whether someone can simply walk onto the property, badge their way past staff, or climb a fence after dark and reach the equipment that keeps water flowing t …
Do You Need a QSA? How to Choose the Right Assessor for Your Firm
by Patrick Hughes on August 11, 2026 at 12:15 PM
If your business stores, processes, or transmits cardholder data, you have almost certainly come across the term QSA. But whether you actually need to hire one, and how to pick a good one if you do, is not always clear. This guide breaks down what a Qualified Security Assessor does, w …
What the Minnesota Water Hack Reveals About OT Security Assessments
by Jesse Roberts on August 5, 2026 at 11:00 AM
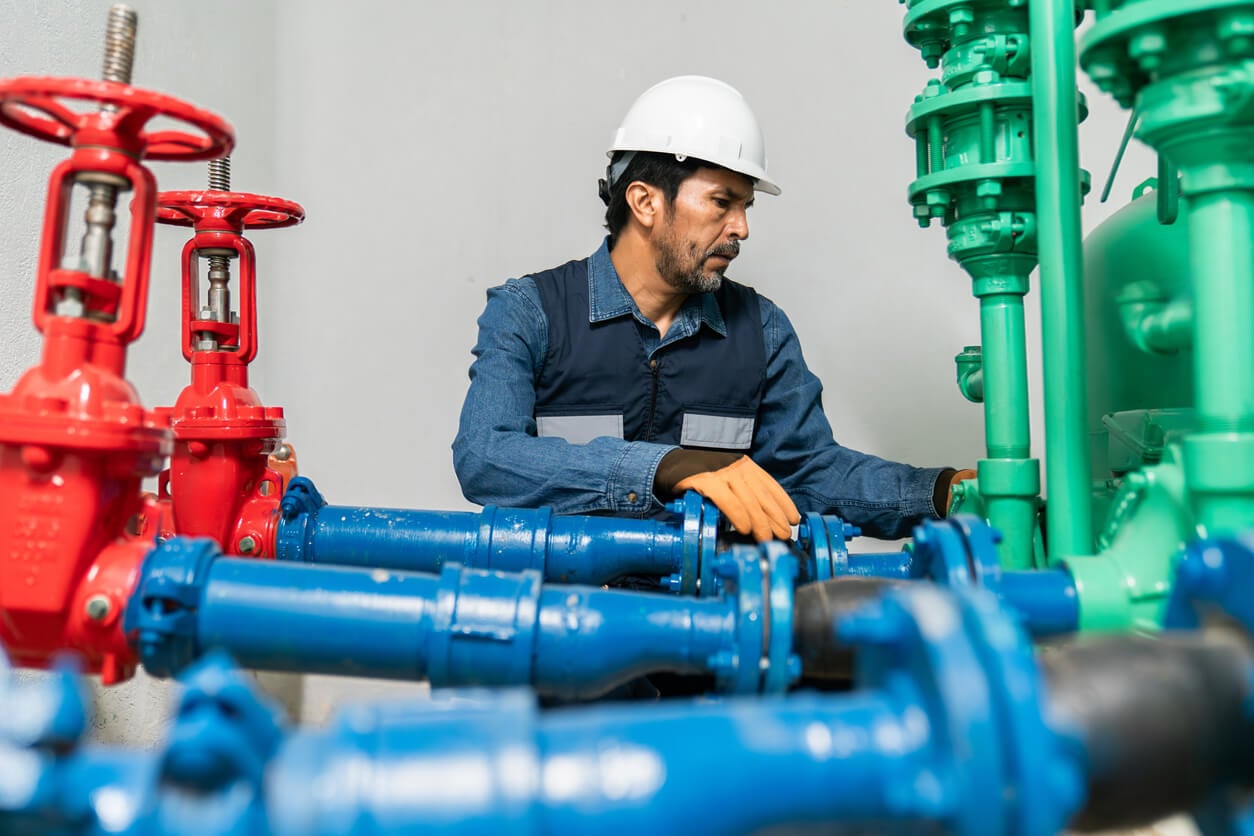
On July 26 and 27, a coordinated cyberattack hit more than 30 community water systems across Minnesota. Our team is trained in running penetration tests against OT and ICS environments, and when we read the reporting on this one, nothing about it was surprising. That's the part that s …
Old Policies, New Technology: Is Your Insurance Actually Ready for AI?
by Kelly O’Brien on August 4, 2026 at 12:00 PM
Most business owners have never read their commercial insurance policies front to back. They renew, file the paperwork, and trust that if something goes wrong, they're covered. For years, that quiet trust extended to artificial intelligence too, even though the word “AI” appeared nowh …
How to Read a SOC 2 Report: A Section-by-Section Guide
by Janelle Lewis on August 3, 2026 at 11:30 AM
A few months ago, at an ISACA event, a woman came up to me for help interpreting her organization's SOC 2 report. She had strong business acumen, but she'd been handed the vendor risk function with almost no background in how to actually read one. That conversation stuck with me, beca …
Mercedes-Benz Dealer ISO 27001 & TISAX Certification Deadline 2026
by Robbie Harriman on July 30, 2026 at 11:00 AM
If you lead IT, security, or compliance at a Mercedes-Benz dealership, you have probably already seen the note buried in your dealer communications: Mercedes-Benz now expects its dealer network to stand up a qualified information security program, backed by ISO 27001, TISAX Level 2 ce …