
What Is a SOC 2 Report and Who Needs One?
by Derek Boczenowski on March 29, 2024 at 11:43 AM
In an era where data security and privacy are paramount, the SOC 2 report emerges as a critical tool for organizations that manage customer data. Tailored to ensure the safeguarding of information, a SOC 2 report not only enhances an organization's credibility but also solidifies its …
NIST Cybersecurity Framework 2.0 – Key Takeaways
by Derek Boczenowski on March 7, 2024 at 1:30 PM
Last week, the National Institute of Standards and Technology (NIST) unveiled the second version of its Cybersecurity Framework (CSF), marking the first major new updates to NIST CSF since the framework's inception ten years ago. Initiated by Executive Order 13636, the development of …
Understanding the Key Differences Between IT Governance & Compliance
by Derek Boczenowski on February 2, 2024 at 3:00 PM
In the dynamic landscape of business expansion and evolution, distinguishing between IT governance and compliance becomes not just beneficial, but essential. While both are pillars in safeguarding organizations against a myriad of risks, they differ in their core objectives, methodolo …
What is Protected Health Information (PHI)?
by Derek Boczenowski on January 3, 2024 at 4:30 PM
Protected Health Information (PHI) is a key element in healthcare, governed by stringent legal and ethical standards. This blog explores what PHI encompasses, its significance under HIPAA regulations, and the crucial distinction between PHI and electronic PHI (ePHI). The blog also del …
Cell Phone Usage at Work & HIPAA Compliance: Uncovering the Risks
by Derek Boczenowski on November 20, 2023 at 1:00 PM
The healthcare industry is increasingly embracing mobile technology, integrating smartphones, tablets, and other portable devices into everyday operations across hospitals, clinics, and other workplaces. This shift towards mobile integration, while offering substantial benefits, also …
Not Using Multifactor Authentication? Your Days Are Limited!
by Derek Boczenowski on February 22, 2023 at 2:30 PM
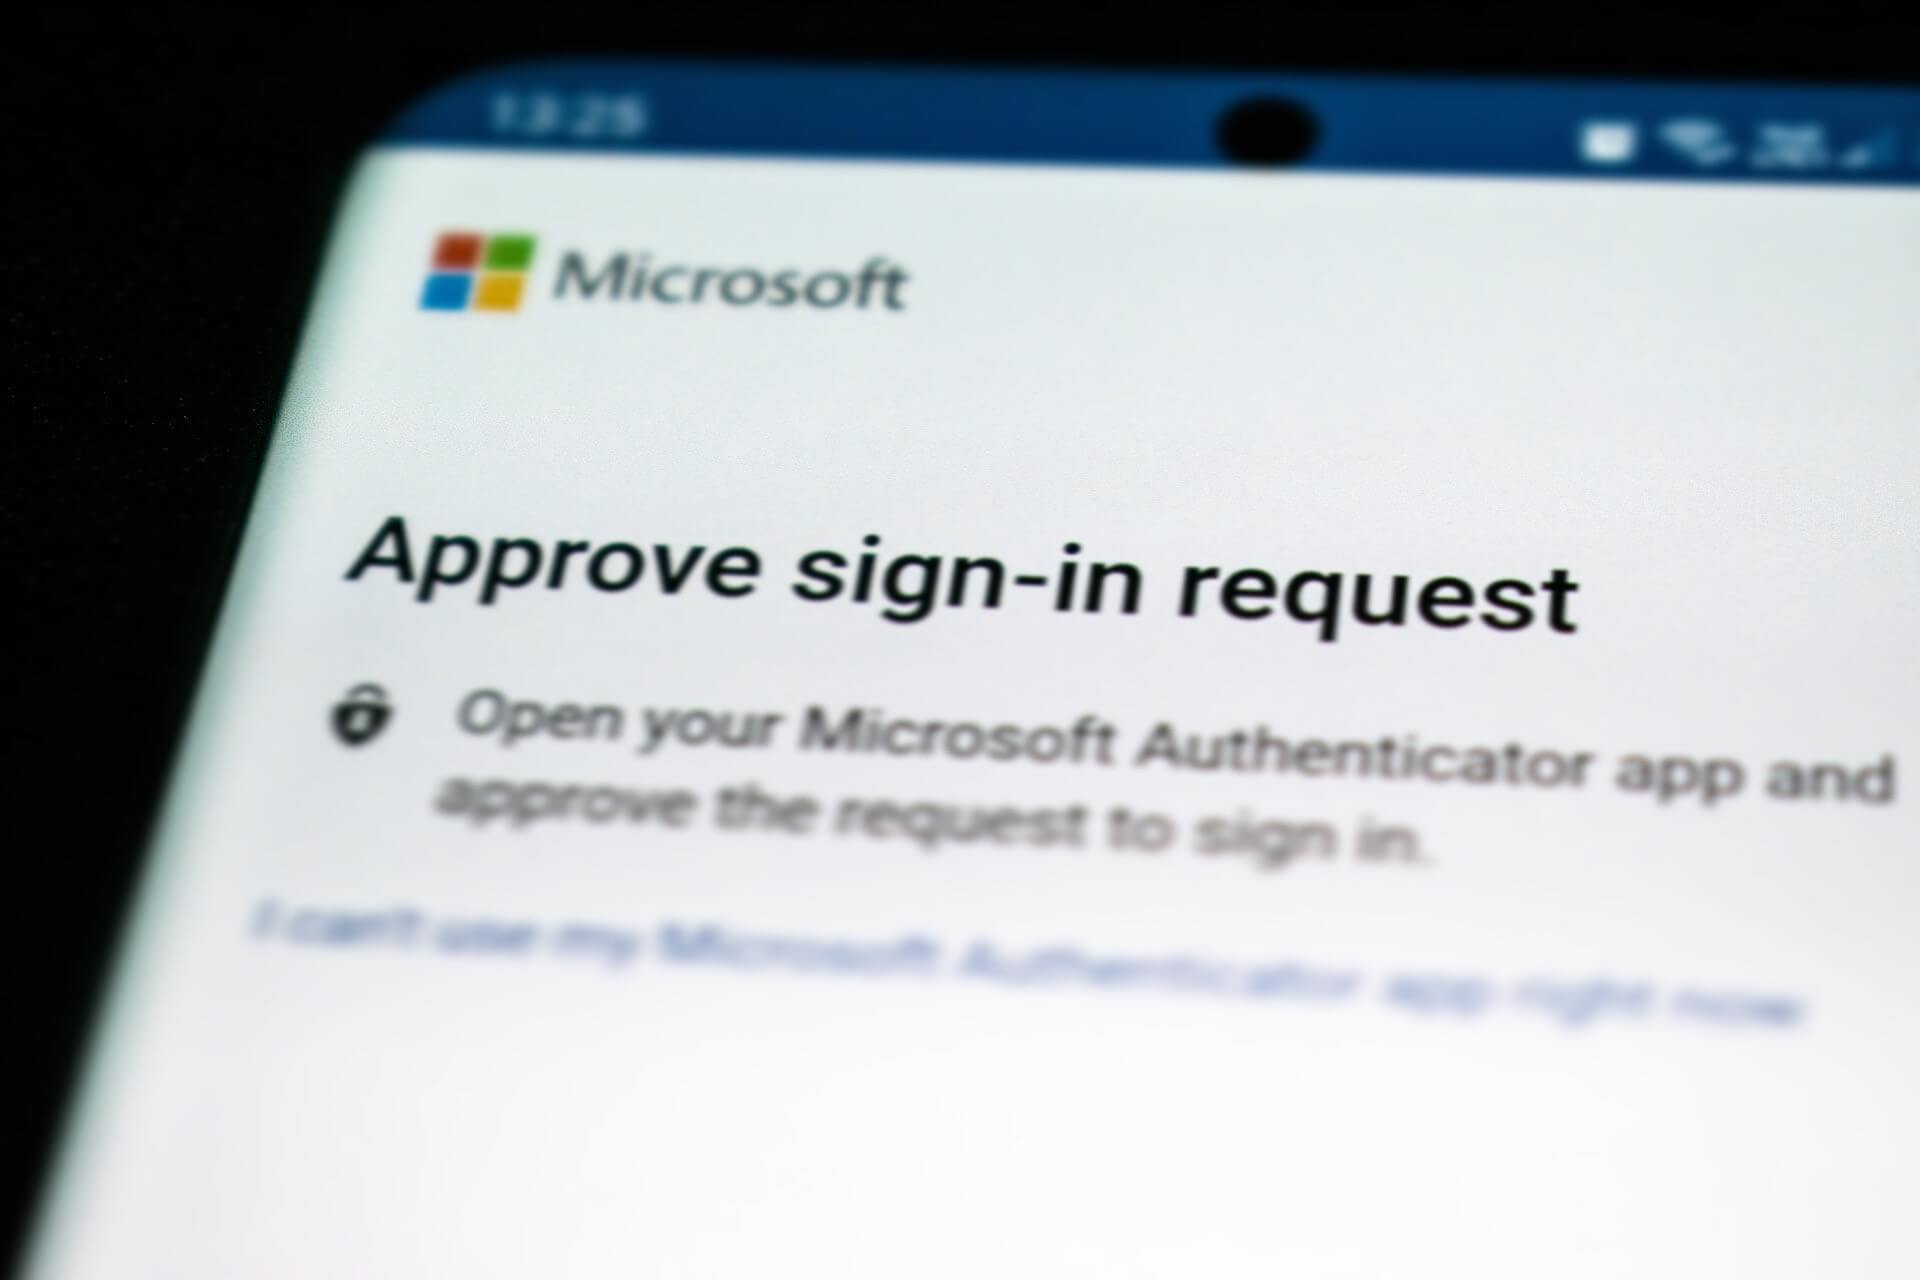
Despite the fact the multifactor authentication (MFA) has been around for decades at this point, the majority of both business and personal logins only use it when absolutely necessary. The complaints are well known; it takes too long to login, if I forget my phone or token I can’t lo …